Public Certificate Creation using win-acme (Optional)
In order to authenticate using a certificate, both a public and a private key are required. The following steps outline how to generate a keystore on the server using Win-ACME and later use KeyStore Explorer to manage the public and private keys. This step is optional if the client already has a trusted certificate issued by a recognized Certificate Authority (CA).
Download win-acme from official website (https://www.win-acme.com/)
The downloaded file should be in ZIP format. Hence, extract the contents of the file and place them in the middleware server, e.g., c:/wacs
now open command prompt as administrator and navigate to folder location c:\wacs
execute wacs.exe
choose "M" from menu.
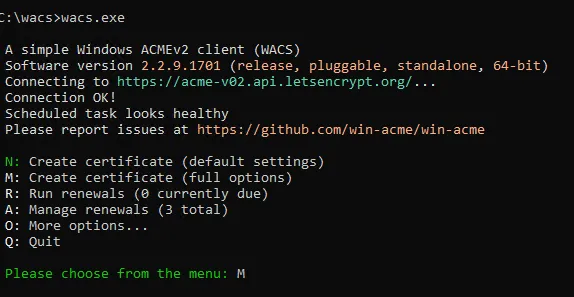
type 2 to manually entered all the domain.
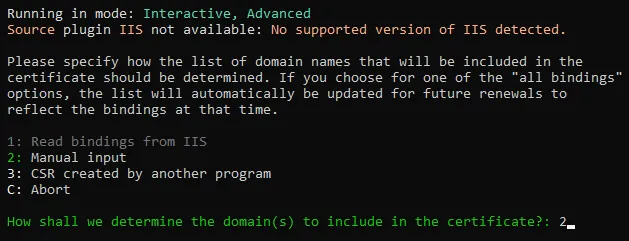
Now provide DSN name. you can enter multiple seprated by ,.
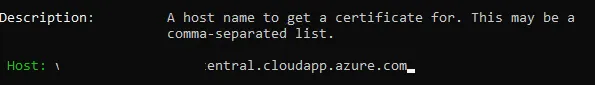
The next prompt will ask for the friendly name of the generated certificate. Enter suitable name

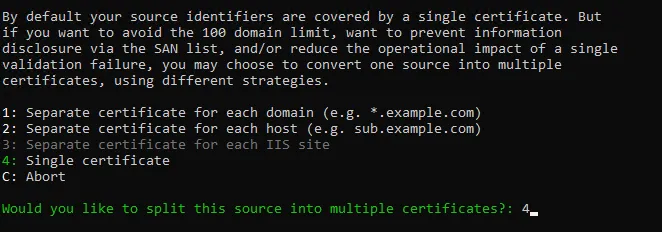
Type 4 to generate a single certificate.
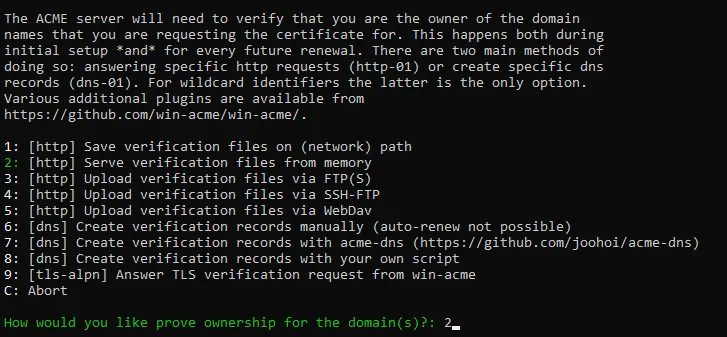
Type 2 for "Serve verification files from memory"
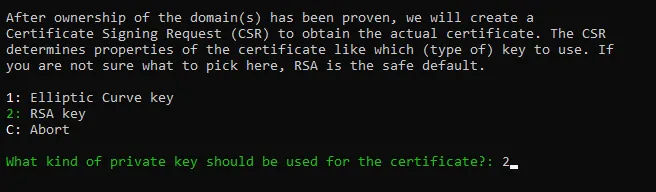
Type 2 for RSA Key.
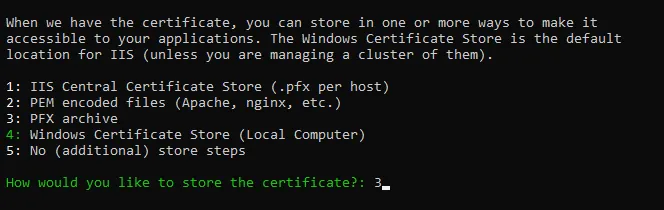
Type 3 to generate PFX archive
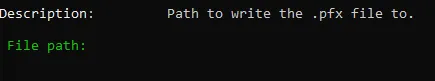
Next provide desired folder path where pfx file will be saved.
Next 1 to not associate a password or 2 to protect pfx with password. Here I will choose 1.
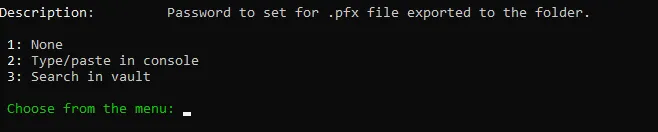
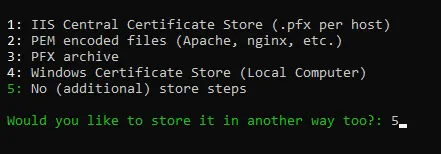
Now select 5 for No additional store steps.
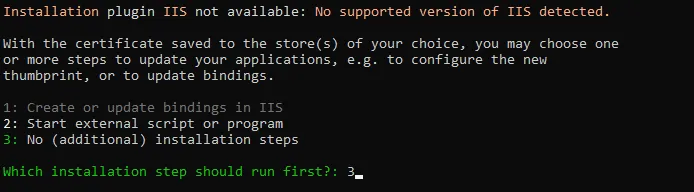
Type 3 for No Addtional installation steps.
Now it will run generate pfx file in desired location.
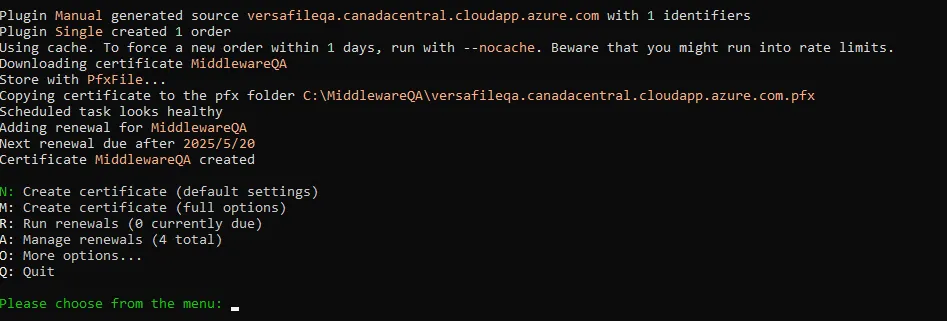
Press Q to Quit.
Now, the PFX file has been generated. It is time to extract the public and private keys from it. To achieve this, we will use a tool called 'KeyStore Explorer'. It can be downloaded from this link : (https://keystore-explorer.org/downloads.html)
Once downloaded, install it with the default settings
open KeyStore Explorer.
Drag and drop the newly generated PFX file onto the KeyStore Explorer window, or choose to open an existing keystore.
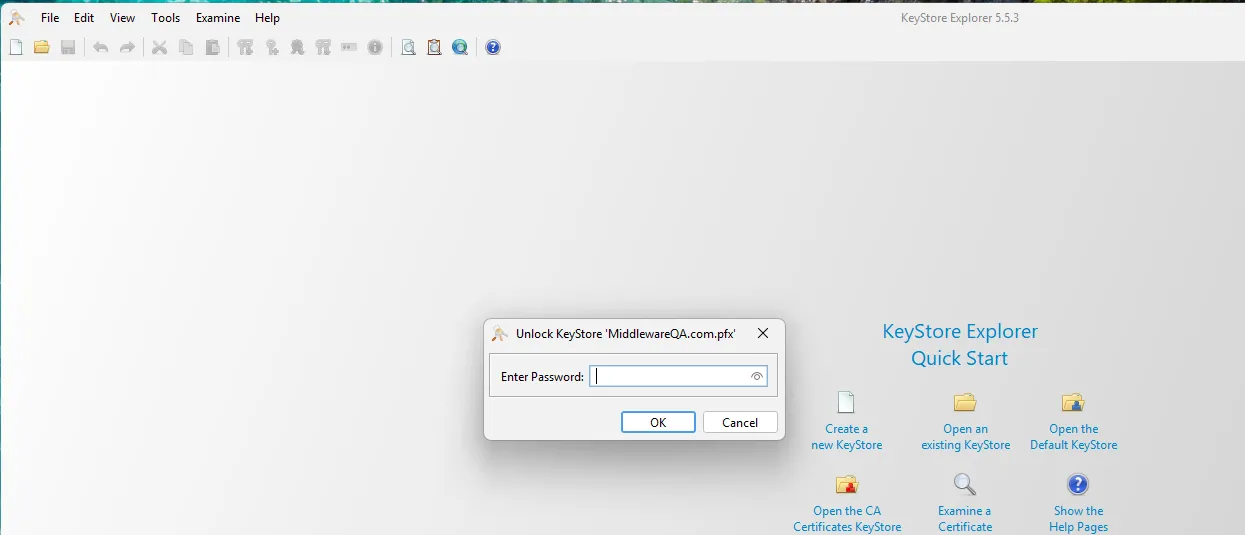
Enter the password if provided at the time of PFX creation; otherwise, press Enter or click OK. You should be able to see the certificate chain details with the DNS name.

Right-click on the certificate chain, select 'Export' → 'Export Private Key' to export the private key.
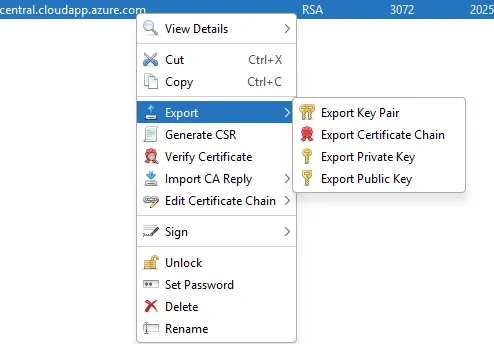
For the password, enter the password you provided earlier, or press Enter or click OK.
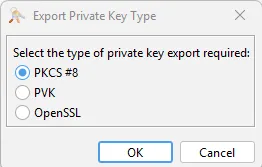
Select 'PCS#8' for the private key export type and click OK.
Next, it will provide an option to encrypt and specify the export file location. For this, we will use an unencrypted private key.
Uncheck 'Encrypt.'
In the 'Export File' field, change the folder location and file name.
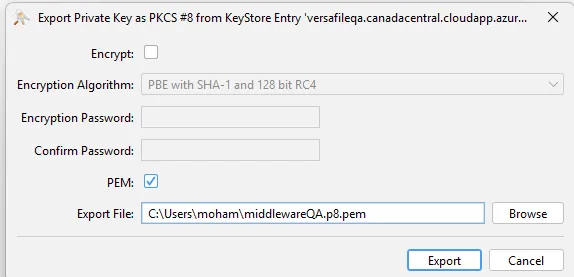
Click 'Export,' and a success message should appear.
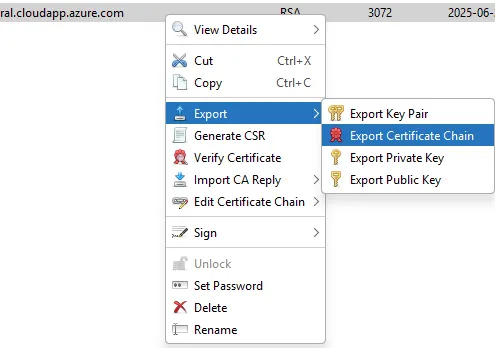
Now, generate the public certificate by right-clicking, selecting 'Export' → 'Export Certificate Chain.'
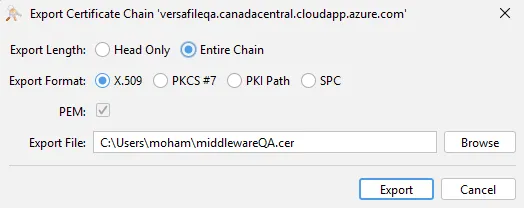
Next, select 'Entire Chain' in the Export Length, 'X.509' in the Export Format, and change the folder location and file name in the 'Export File' field.
Click on 'Export,' and a success message should appear.
Now, go to the folder location, and there should be two files exported.
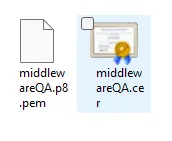
The PEM file represents the private key, and the CER file is the public certificate. The next step is to place those files under the config folder of the Middleware installation and modify the init file:
- 'sharepoint.cert.privatekey.path' to the private key path
- 'sharepoint.cert.publickey.path' to the public certificate path
- 'sharepoint.cert.privatekey.encrypted' to 'Yes' or 'No' if the private key is encrypted
- 'sharepoint.cert.privatekey.password' to the decrypted private key password via the Encryption utility
For more details, please refer to the 'SharePoint M365 Endpoint' section."
SharePoint (SP365) Authentication Configuration
Authentication Modes
App-Based Authentication Enables service-to-service communication without user interaction. sp365.sharepoint.appBasedAuthentication = true
Certificate-Based Authentication Uses certificates for enhanced security. sp365.sharepoint.certBasedAuthentication = true
OAuth 2.0 Parameters
Grant Type sp365.sharepoint.granttype = client_credentials
Client Assertion Type sp365.sharepoint.client.assertion.type = urn:ietf:params:oauth:client-assertion-type:jwt-bearer
Resource URL sp365.sharepoint.resource.url = https://graph.microsoft.com
Certificate Configuration
Private Key Path Path to the private key file used to sign JWTs. sp365.sharepoint.cert.privatekey.path = <path-to-private-key.pem>
Private Key Encryption Indicates whether the private key file is encrypted. sp365.sharepoint.cert.privatekey.encrypted = YES
Private Key Password (use encryption utility) Provide only if encryption is enabled. sp365.sharepoint.cert.privatekey.password = <secure-password>
Public Key Path Path to the public certificate used to validate signatures. sp365.sharepoint.cert.publickey.path = <path-to-public-cert.cer>
JWT Settings
Type sp365.sharepoint.jwt.type = JWT
Algorithm sp365.sharepoint.jwt.algorithm = RS256
Expiration Example: 1 hour = 3600000 ms sp365.sharepoint.jwt.expiration.millisec = 3600000